
Requirements Engineering
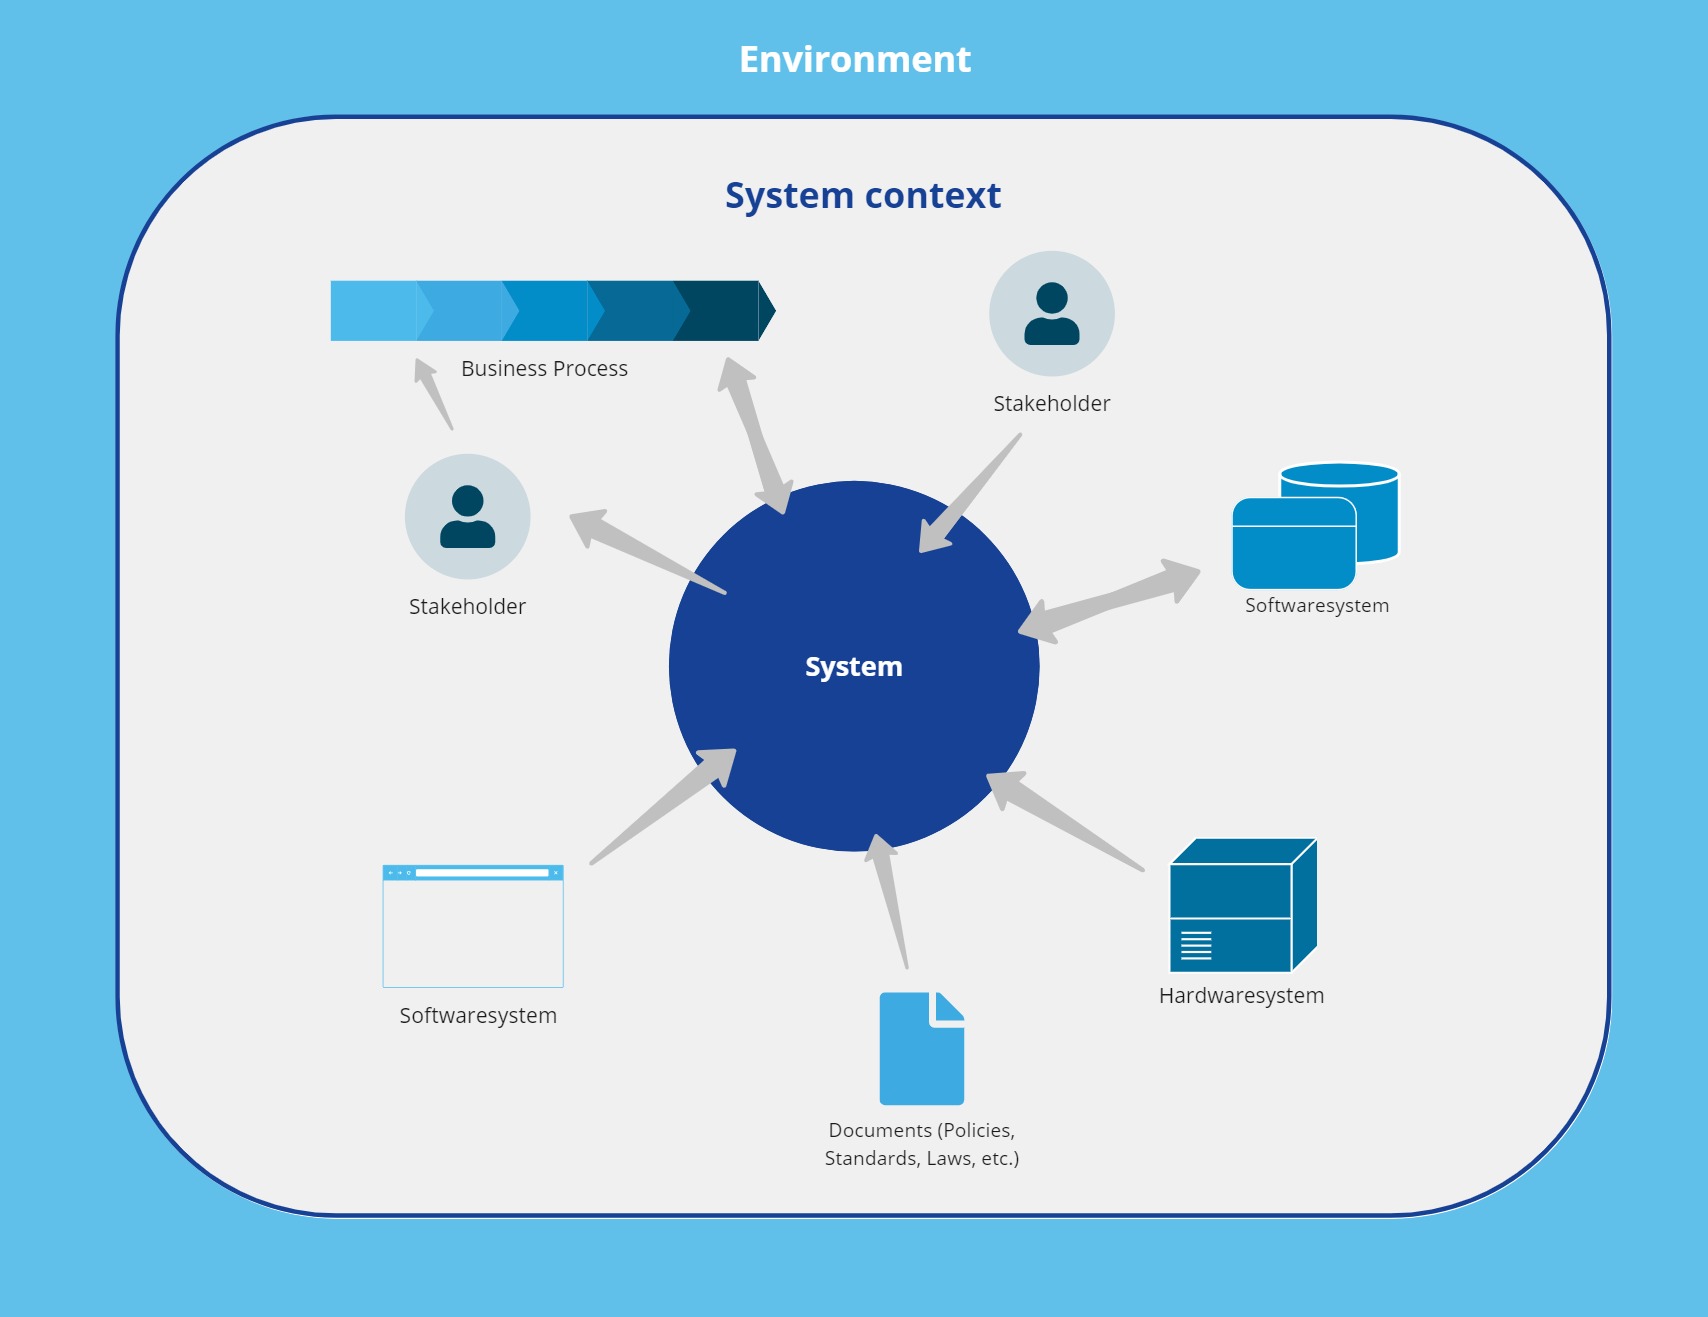
Building a sustainable and long-lasting solution starts with deeply understanding the requirements. The foundation lies in the business process. I can help break down these processes into requirements that are easily understandable by business users, because they are formulated in business language. With a clear understanding of the requirements, the problems to be solved or the tasks to be automated become explicit. My goal is to ensure that all stakeholders share a common understanding of the problem — preventing solutions that miss the actual business need.
In-depth analysis Deep dive into the business processes to analyze the needs of organizations for GRC systems
Stakeholder alignment Requirements are challenged and refined through structured dialogue to achieve a shared understanding among all stakeholders.
Conducting workshops Conducting sessions to analyse and refine requirements, discuss objectives and alternatives.
Documentation Transforming discussions and insights into clear, understandable, actionable, and organized requirements documents. Documentation is key for every subsequent step and serves as a reference throughout the design, implementation and test phases. Requirements should be mapped to design and implementation elements.
Traceability In the further progress it is vital to map requirements to design and implementation elements. This ensures that as systems evolve, any implemented item can be traced back to its original requirement. Externalizing this knowledge reduces reliance on tacit understanding, making it clearer, even years later, why the system was designed in a particular way.
Specialization
I am specialized in requirements analysis for Governance, Risk and Compliance (GRC) / Integrated Risk Management (IRM) tools as well as for interfaces between systems. Within the GRC domain I am experienced in defining requirements for tools to support:
- IT Risk Management
- Information Security Management System
- Enterprise Risk Management
- Internal Control System
- Business Continuity Management
- Operational Loss Events (Asset Management)
- Risk Bearing Capacity